
US Water Systems Face Growing Cyberattack Risks
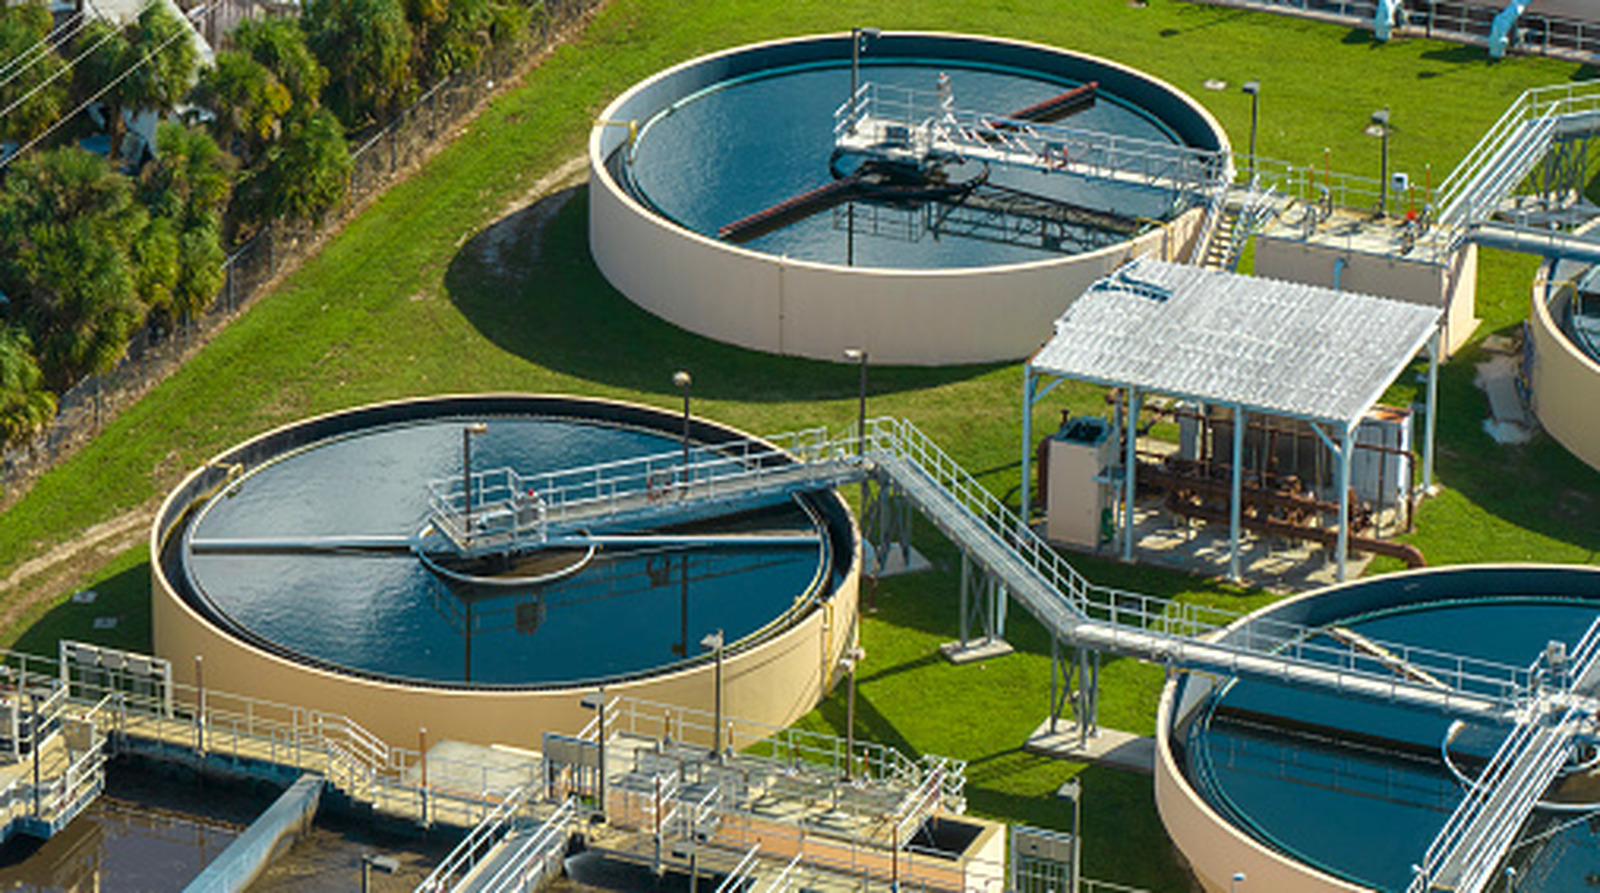
Cover image from engadget.com, which was analyzed for this article
Recent hacks and suspected Iranian activity highlight vulnerabilities in critical water infrastructure nationwide.
PoliticalOS
Saturday, August 1, 2026 — Tech
The two outlets examined provided no usable information on the water system cyberattacks. Readers seeking details on the incidents, their scope, or federal responses must consult other sources that actually reported the events.
What outlets missed
Neither provided outlet delivered any reporting on the water system incidents despite the topic summary. The Dispatch entry contained only a headline and unrelated material, leaving readers without details on affected states or federal assessments. Slate published an unrelated advice column with no connection to infrastructure security. This left core elements such as the number of states involved and technical descriptions of the hacks entirely absent from both sources.
Iran Likely Behind Series of Cyberattacks on Water Systems in Seven States
The recent cyberattacks targeting water and wastewater utilities across seven states have drawn renewed attention to the vulnerabilities in American critical infrastructure, particularly as tensions with Iran escalate into open conflict. A memo obtained by investigators links dozens of incidents in Minnesota alone to Iranian actors, marking the first official documentation tying the group to what appears to be a coordinated campaign against U.S. systems. The attacks, which began surfacing around July 27, have involved hackers gaining remote access to internet-facing devices, altering IP addresses and passwords, and disrupting operators ability to monitor and control water flows.
Authorities including the FBI and Environmental Protection Agency issued a public service announcement detailing how the intrusions focused on programmable logic controllers, or PLCs, common in industrial settings. Victims reported immediate effects such as flooding and sudden drops in water pressure, outcomes that could allow untreated groundwater to enter pipes and compound public health risks. While the precise number of affected facilities remains under review, the incidents span multiple states and align with patterns seen in prior Iranian-linked operations that prioritize disruption over outright data theft.
Historical records show Iranian hackers have repeatedly tested U.S. targets over the past decade. Between 2011 and 2013, seven individuals tied to Iranian government entities and the Islamic Revolutionary Guard Corps faced charges for distributed denial-of-service attacks that temporarily disabled websites at 46 financial institutions, costing banks and customers tens of millions in recovery efforts. The same indictment referenced an attempt to access controls at New Yorks Bowman Avenue Dam, where operators could view water levels and other operational data. More recent activity has included scans of accessible systems for known weaknesses, often timed to coincide with geopolitical friction.
Investigators are still confirming whether the latest water utility breaches stem directly from Iranian operators or represent an effort to mimic their tactics and sow confusion during the ongoing U.S.-Iran conflict that began roughly six months ago. Iran has consistently denied involvement in such activities. Regardless of attribution, the episodes highlight how readily available tools and exposed industrial control systems can be leveraged against essential services that millions rely on daily.
Policy responses have centered on immediate defensive measures. Officials recommend segmenting networks with secure gateways and firewalls to limit direct internet exposure, enforcing stronger password protocols, and applying access control lists that restrict communications to authorized devices only. These steps echo longstanding cybersecurity guidance yet remain unevenly adopted across smaller utilities that often operate with limited technical staff and older equipment.
Broader questions persist about how the United States protects infrastructure that sits at the intersection of public health, local governance, and national security. The incidents arrive amid parallel developments in artificial intelligence and automated systems, where even defensive tools can introduce new risks if not properly contained. They also underscore the challenge of deterrence when attacks produce visible but non-catastrophic effects that fall short of triggering full-scale retaliation.
As agencies continue their probes, attention is likely to shift toward funding mechanisms that could help under-resourced utilities harden their systems without passing costs directly to ratepayers. The pattern of probing and incremental disruption suggests these threats will recur, requiring sustained coordination rather than one-time alerts.
You just read Liberal's take. Want to read what actually happened?
More in Technology

Democratic Wins Heighten Scrutiny of Data Center Expansion
Newly empowered Democrats signaled opposition to rapid AI data center growth on public lands and elsewhere. This contributed to market pressure on chipmakers and infrastructure firms.
Nvidia Faces Added Scrutiny on AI Shipments After Midterms
Nvidia faces increased monitoring of accelerator shipments amid smuggling concerns to China. Broader regulatory uncertainty from the election weighed on the sector.

Google Ties Search Access to AI Opt-In for K-12 Schools
Google will turn its AI tools off by default for K-12 students starting in 2027 and will restrict Search access for schools that fully block AI. The policy reflects deeper integration of AI into core products. Right-leaning New York Post and tech coverage noted the changes.

FBI Ties $6.3 Billion Binance Hack to North Korea; Pyongyang Fires Missiles
The FBI linked the theft of over $6 billion in cryptocurrency from Binance to North Korea's Lazarus Group, citing social engineering. Laundering the funds is expected to take months. Engadget, New York Post, and other outlets reported on the investigation.
The Compass
You just read five takes on one story.
What's your take? Find your political shape in a few minutes.
Take the test