
US Water Systems Face Growing Cyberattack Risks
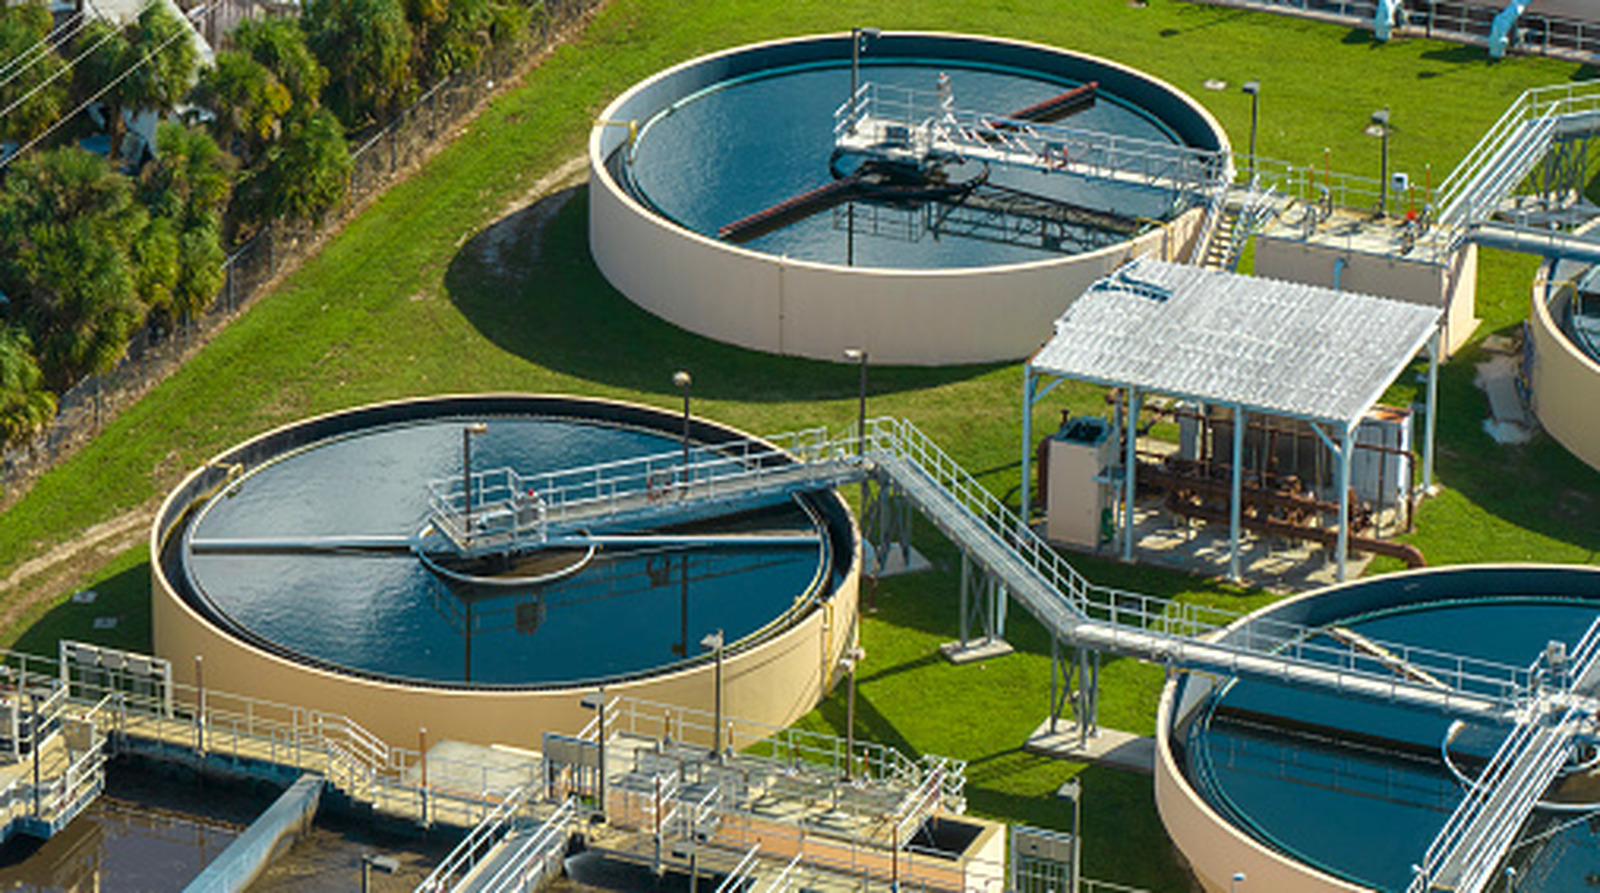
Cover image from engadget.com, which was analyzed for this article
Recent hacks and suspected Iranian activity highlight vulnerabilities in critical water infrastructure nationwide.
PoliticalOS
Saturday, August 1, 2026 — Tech
The two outlets examined provided no usable information on the water system cyberattacks. Readers seeking details on the incidents, their scope, or federal responses must consult other sources that actually reported the events.
What outlets missed
Neither provided outlet delivered any reporting on the water system incidents despite the topic summary. The Dispatch entry contained only a headline and unrelated material, leaving readers without details on affected states or federal assessments. Slate published an unrelated advice column with no connection to infrastructure security. This left core elements such as the number of states involved and technical descriptions of the hacks entirely absent from both sources.
Water Utilities Across Seven States Targeted in Cyberattacks as US-Iran War Continues
Federal investigators are examining a wave of cyberattacks that struck water and wastewater systems in at least seven states since late July, with early indications pointing to actors linked to Iran. The incidents have disrupted operations at multiple utilities, causing flooding and drops in water pressure that left some facilities struggling to maintain basic monitoring and control functions.
A memo obtained by reporters details how the attacks focused on internet-facing devices running programmable logic controllers. Intruders changed IP addresses and passwords, locking out legitimate operators and forcing manual interventions. Victims reported degraded service across facilities in Minnesota and other states, though no widespread contamination or prolonged outages have been confirmed so far.
The timing coincides with an ongoing US military conflict with Iran that began nearly six months ago. Officials have not released conclusive forensic proof tying the latest intrusions directly to Tehran, and investigators are weighing whether the perpetrators may have sought to mimic Iranian tactics to heighten tensions. Iran has consistently denied involvement in any such operations.
Past attributions of Iranian-linked hacking have included distributed denial-of-service campaigns against major US banks between 2011 and 2013 that temporarily disabled customer access and generated millions in recovery costs. A separate 2013 case involved access to a small New York dam's control system, though no physical damage occurred. Those earlier episodes relied on indictments naming individuals tied to Iranian government entities, yet technical attribution in real time often remains contested and can take months to solidify.
Authorities have issued public guidance urging utilities to segment networks, deploy firewalls, and avoid exposing control systems directly to the internet. The Environmental Protection Agency and FBI have stressed basic measures such as strong passwords and access controls, measures long recommended after previous infrastructure probes. Some facilities affected in the current wave lacked even these standard protections, according to preliminary assessments.
The broader context includes heightened US-Iran friction stemming from the current war, which has already produced reciprocal accusations of sabotage and cyber activity. Skeptics note that rushed public attributions during active conflicts can serve domestic political purposes, particularly when evidence chains are still under review. Independent analysts have pointed out that multiple state and non-state actors possess the capability to spoof Iranian signatures, complicating rapid conclusions.
No deaths or major public health emergencies have been linked to the water system intrusions to date. Utilities continue to restore remote access while law enforcement collects logs and traces command-and-control infrastructure. Further official statements are expected once investigators complete initial technical analysis, though full public confirmation of responsibility may remain elusive for weeks.
You just read Progressive's take. Want to read what actually happened?
More in Technology

Democratic Wins Heighten Scrutiny of Data Center Expansion
Newly empowered Democrats signaled opposition to rapid AI data center growth on public lands and elsewhere. This contributed to market pressure on chipmakers and infrastructure firms.
Nvidia Faces Added Scrutiny on AI Shipments After Midterms
Nvidia faces increased monitoring of accelerator shipments amid smuggling concerns to China. Broader regulatory uncertainty from the election weighed on the sector.

Google Ties Search Access to AI Opt-In for K-12 Schools
Google will turn its AI tools off by default for K-12 students starting in 2027 and will restrict Search access for schools that fully block AI. The policy reflects deeper integration of AI into core products. Right-leaning New York Post and tech coverage noted the changes.

FBI Ties $6.3 Billion Binance Hack to North Korea; Pyongyang Fires Missiles
The FBI linked the theft of over $6 billion in cryptocurrency from Binance to North Korea's Lazarus Group, citing social engineering. Laundering the funds is expected to take months. Engadget, New York Post, and other outlets reported on the investigation.
The Compass
You just read five takes on one story.
What's your take? Find your political shape in a few minutes.
Take the test